Compliance and Security
Built for trust accounting that has to balance, to the cent and to the law.
Every Australian state and territory. Two security certifications.
Strata firms handle obligations that have to balance, to the cent, to the law, every period. The platform that runs them has to meet a higher bar than off-the-shelf business software: auditable, certified, and aligned to the laws of every jurisdiction the firm operates in.
Certifications
ISO 27001 and SOC 2 Type 2. Both current, both externally audited.
ISO/IEC 27001 · Information security management
ISO 27001
StrataMax is ISO 27001 certified across the platform and supporting infrastructure, with annual renewal by an accredited external auditor.
AICPA · Trust services criteria
SOC 2 Type 2
SOC 2 Type 2 covers both the design and operating effectiveness of our controls over a continuous review period. Reports are available under NDA to qualifying procurement teams.
Every state
Every state. Every territory. One platform.
Strata law is not one law. The accounting module is built to the standards and legislation of every Australian state and territory, and updated whenever the rules change. One less thing for your team to worry about.
Built for compliance
Aligned to strata legislation in every state and territory.
Always up to date
Regulatory changes monitored
One platform
The same trust ledger and audit trail across every jurisdiction.
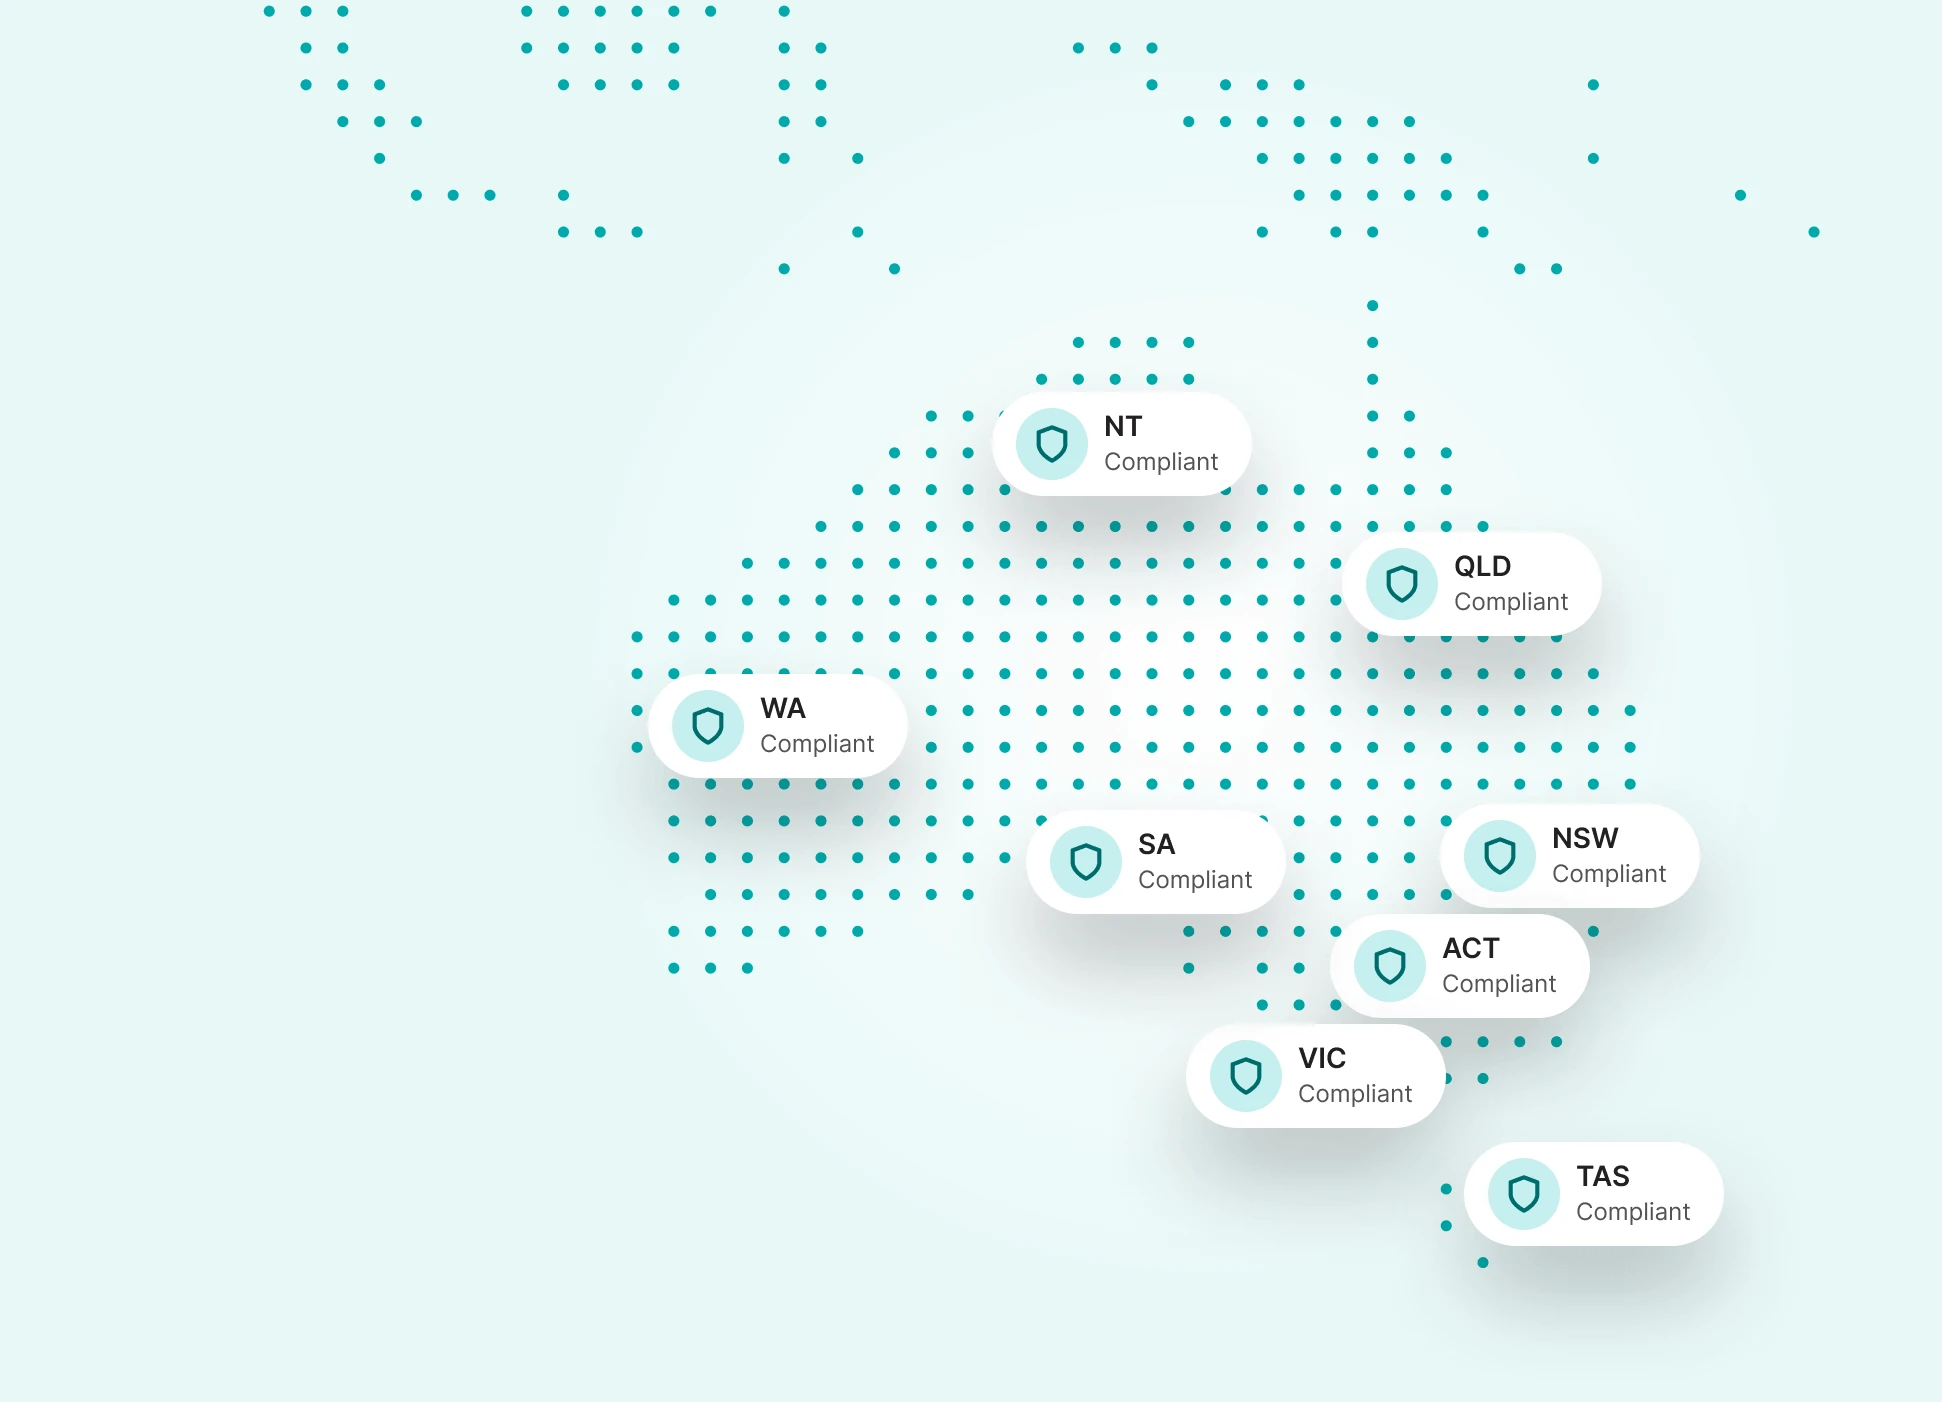
StrataMax compliance coverage by jurisdiction: Western Australia, Northern Territory, Queensland, New South Wales, Australian Capital Territory, Victoria, Tasmania and South Australia are all compliant.
Data sovereignty
Australian data, in Australian regions, under Australian law.
Customer data is stored in Australian regions. Privacy obligations are governed by the Australian Privacy Principles. Recovery procedures are documented and tested.
Australian regions
Customer data is stored in Australian regions, with operational controls aligned to the same trust-accounting environment the platform runs on.
Australian privacy obligations
Privacy handling sits under the Australian Privacy Principles, and the security brief is available upon request.
Documented recovery procedures
Backups run daily and disaster recovery is tested at least annually, with defined RTO and RPO targets. The full detail (cadences, retention, runbooks) is on the security page.
Operational security
Behind the certifications: the operational layer.
The certifications above prove the controls exist. The security page documents how they run, from encryption through to business continuity.
01
Encryption
At rest and in transit. Keys rotated on a documented cadence.
02
Access controls
Role-based, least-privilege. Multi-factor authentication enforced.
03
Audit logs
Every change to customer data, logged and retained.
04
Vulnerability management
Independent penetration testing on a regular cadence.
05
Incident response
Documented plan. Customer notification commitments published.
06
Employee security
Background-checked staff. Continuous training. Secure development.
07
Business continuity
Backups tested. DR plan exercised annually.
BOOK A DEMO
We’re here to help. Not upsell.
Book a working session with our team. See how StrataMax handles the workflows your team runs every day, and ask the migration questions that matter.
- Onshore Aussie team
- Strata specialists
- Since 1992
What to expect in your demo
- Walk through your real workflows
- Test your portfolio fit
- Ask the migration questions
- Meet your Client Success Manager